
Customer Service AI Agents
Indirect injection through inbound emails and tickets can redirect a support agent into exfiltrating CRM data. We detect and block it before it reaches production.

We look at how your AI interacts with users, data, and outside tools to spot vulnerabilities. You get a picture of what is in danger and what should be fixed right away.

We put your AI models through real-world attack scenarios, including jailbreaks and malicious prompts, to uncover weaknesses that could lead to unsafe responses or security breaches.

Your AI agents can access data, use tools, and take action. We test these capabilities to catch unauthorized access, risky actions, and security gaps before they cause damage.

Attackers hide instructions in papers, sites, or messages. We check how your AI deals with these tricks. We help stop attackers from taking control of its behavior.

We check if AI can expose customer information, confidential records, or API keys. Our testing helps you spot data leaks and keeps information safe.

We check the knowledge sources your AI connects to for content that shouldn't be there and information you can't trust. This ensures bad information doesn't make it into the AI's answers.

We test how AI agents talk, share data, and use tools. This helps stop one AI agent or integration from putting the whole workflow in danger.
We don't just identify vulnerabilities. We help your team fix critical issues, retest security controls, and address new threats as your AI evolves, supported by our AI governance consulting services.
Indirect injection through inbound emails and tickets can redirect a support agent into exfiltrating CRM data. We detect and block it before it reaches production.

Jailbreaks can push a coding agent into executing malicious shell commands. Tool sandboxing and strict execution policies stop the sandbox escape.

A compromised sub-agent can push malicious instructions to the orchestrator. Cryptographic message signing breaks the attack chain across the network.

Adversarial queries can pull confidential sections out of a RAG index. Output DLP filtering at the response layer prevents the data leak.

Tool abuse can manipulate a finance agent into approving transactions outside its authorised scope. Hard transaction limits and scoped IAM stop it.

Social engineering through an HR agent conversation can extract employee PII. Output PII detection and content filtering keep responses GDPR-safe.
Our AI Red Team Services test agents that handle payments, KYC, and customer records to find security gaps. We use transaction limits, scoped access, and audit-ready logging. We also strengthen security across our AI agents for banking solutions.
PHI-aware output filtering, restricted data access, and prompt injection testing help prevent clinical AI agents from exposing sensitive patient information.
Agents handling supplier feeds, customer reviews, and messages can be exposed to hidden malicious instructions. We test these entry points to prevent unauthorized actions and data leaks.
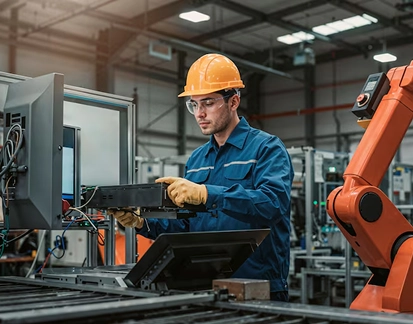
AI agents connected to MES, SCADA dashboards, and maintenance systems need tighter controls. We test tool permissions, access limits, and unusual actions to reduce operational risks.
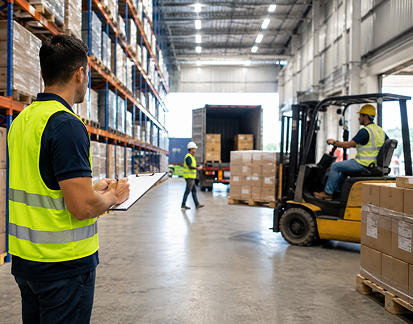
Agents working across TMS, WMS, and carrier APIs undergo AI security testing for tool misuse and privilege escalation before they can trigger unauthorized shipments or payments.
Claims documents can carry instructions that aim to trick AI agents. We test RAG and document-processing agents for injection, data exposure, and policy bypass before deployment, keeping AI agents protected.
Our approach does more than just run automated scans. We put your AI systems through real-world attack scenarios to find weaknesses that typical security checks often overlook.
Our AI red-teaming solutions assess risks using OWASP LLM guidance and MITRE ATLAS, helping you identify prompt injection, data exposure, and other critical AI security threats.
One security control isn't always enough. Through our enterprise AI integration services, we help strengthen access, inputs, outputs, and monitoring to reduce risks across your AI systems.
Finding a vulnerability is the start. We give you results, simple fixes you can use, and a chance to check back to test again. This way, your team knows exactly what’s been fixed and what still needs work.
Security findings should be useful beyond your technical team. Our AI red teaming services provide clear risk reports that support your security reviews, audit preparation, and AI governance requirements.
AI systems change, and so do the threats targeting them. We help you regularly test new features, integrations, and agent behaviors to catch security weaknesses before they become bigger problems.






Days 1-3: We start by understanding how your AI works, what data it accesses, and which tools it uses. This helps us identify potential attack points and prioritize the risks that matter most to your business.
Days 4-7: Using specialized AI red teaming tools, we scan your models, agents, and connected systems for known vulnerabilities. You get a clear list of security gaps ranked by severity and business impact.
Days 8-14: Our team puts your AI through realistic attack scenarios, including prompt injection, jailbreaks, data leaks, and tool misuse. We focus on finding weaknesses that automated scans might miss.
Weeks 3-5: Finding problems isn't enough. We help strengthen access controls, protect sensitive data, and fix exploitable weaknesses. Our AI readiness assessment services can also help identify broader security and governance gaps.
Week 6: Every critical fix goes through another round of testing. We document what was resolved, highlight remaining risks, and provide a clear security report your team can act on.
Ongoing: New features and integrations can introduce new risks. We help you monitor AI behavior, test important changes, and catch emerging threats before they affect your business.


